v10.0
Blink’s Automated Case Management Process streamlines how security teams ingest, enrich, investigate, and respond to alerts from multiple 3rd-party vendor sources. By automating these tasks end-to-end, it enables faster and more consistent triage of potential threats.
The purpose of Blink’s Automated Case Management Process is to reduce manual overhead, maintain data consistency, and accelerate incident response by connecting alert data with contextual information, enrichment tools, and response actions.
This documentation provides an overview of each stage in the automated case management pipeline, including how alerts are ingested and processed, how observables are enriched, and how response and remediation actions are configured and executed.
Key Stages
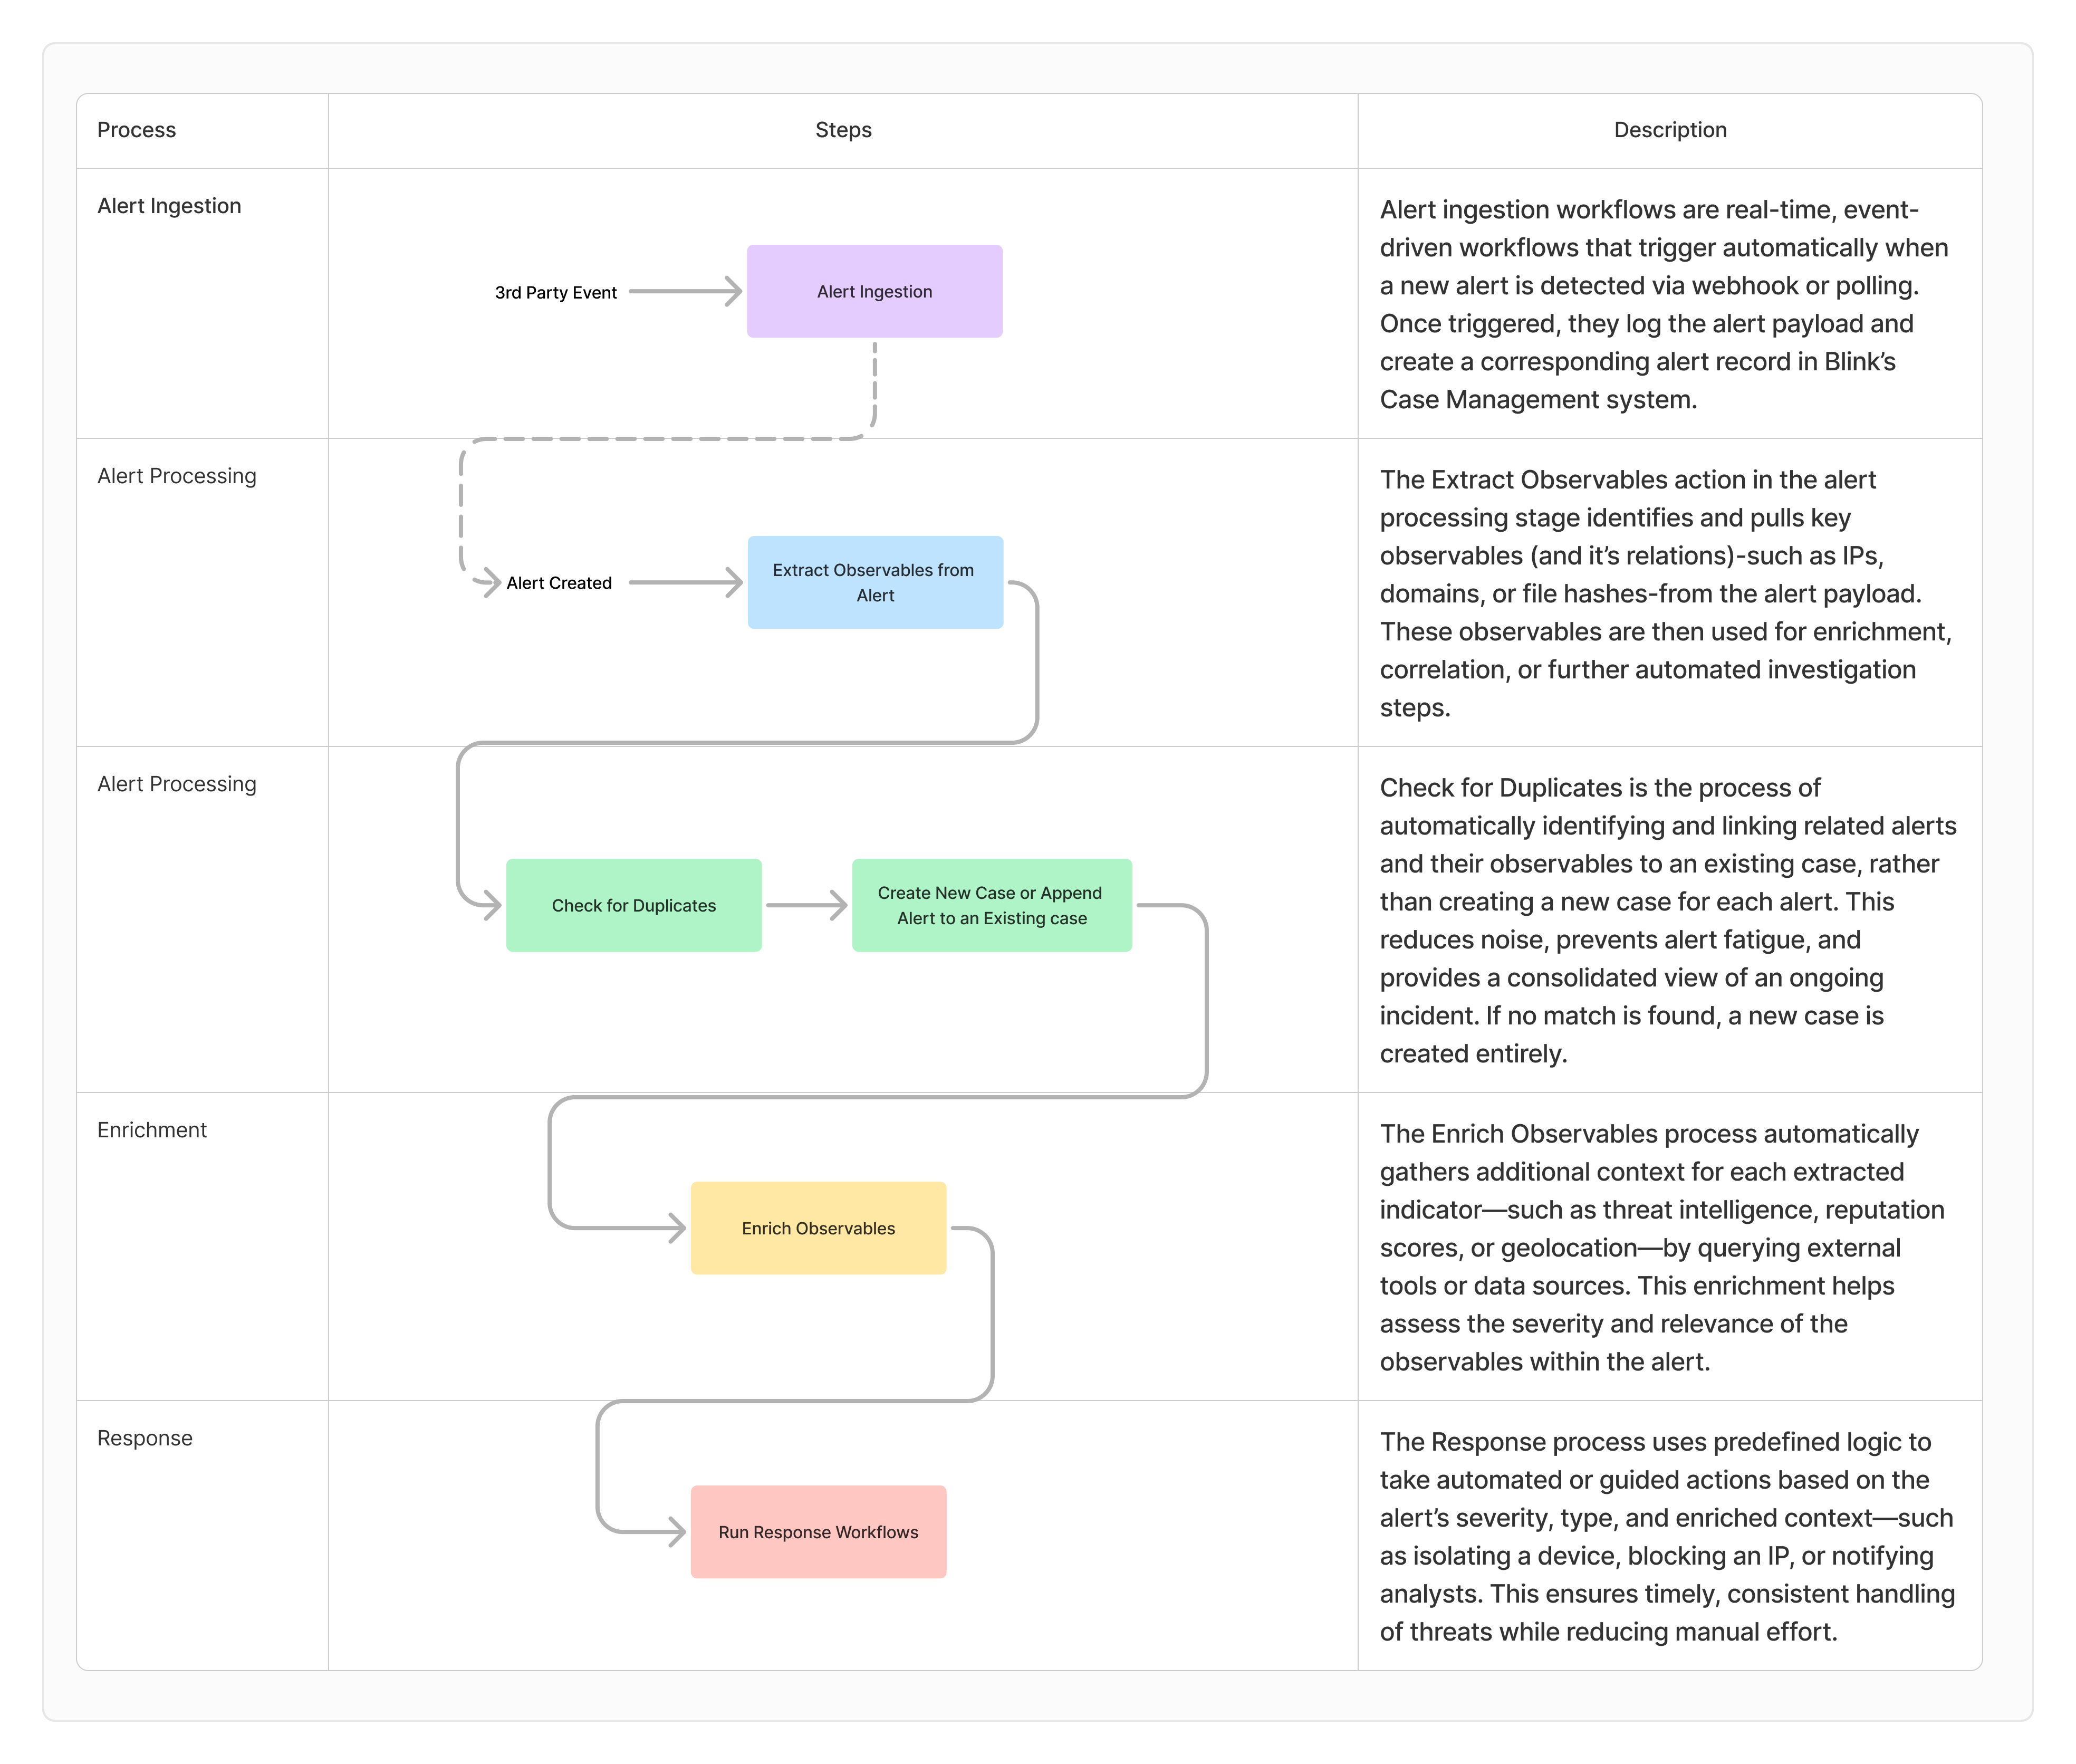
The process is composed of four key stages and is designed to streamline the entire incident handling from alert ingestion to case remediationFlow Diagram Showing the Case Management Automated Processes
The following flow diagram provides an in-depth explanation of how Blink handles alert and case processing, offering insights into each stage of the workflow, associated subflows, data transformations, and examples for testing.