

- Tenant roles grant access across the entire tenant, including settings and global resources.
- Workspace roles control access within individual workspaces, including Case Management and workflow-related permissions.
Case-Level Permissions
By default, workspace roles give users access to all cases in the workspace. If you need to limit users to specific cases instead, use case-level permissions. Case-level permissions are built on two parts that work together:- The
case_management:restrictedpermission is assigned through a workspace role, such as the built-in Case Management Guest role or a custom role. Users with this permission can’t see cases by default. They can only view and edit cases that are explicitly shared with them or their groups, including any linked entities. - Case sharing is how you grant access to individual cases. When you share a case, you choose the permission level the user gets on that case:
Viewer,Editor, orEditor + Close.
Standard Access vs. Restricted Access
How Access Is Determined
A user’s access to a case comes from their workspace role and, for restricted users, from how the case was shared with them:- A user with standard access can see every case in the workspace. Sharing a case with them doesn’t limit what their role already allows. For example, a user with the Owner role who is invited to a case as a
Viewercan still edit it. - A user with restricted access can see only the cases shared with them or their groups, with the permission level the case was shared with.
- Invitees outside your workspace or without a Blink account are created as Guest users when you share a case with their email address, and can access only the cases shared with them.
What Case Access Includes
Permissions are set only at the case level. Items linked to a case don’t have permissions of their own: access to them follows from access to the case. When a case is shared with a user, they get access to everything linked to that case, including:- Alerts
- Tasks
- Comments
- Attachments
- Observables
- Linked cases and other linked entities
- The case timeline
Viewer, Editor, and Editor + Close permissions apply to the case and to the items linked to it:
You can’t share a case while restricting access to individual items in it. For example, you can’t share a case but hide its comments or attachments. If a user shouldn’t see an item linked to a case, don’t share that case with them.
What Restricted Users Can’t Do
Even withEditor or Editor + Close permissions on a case, a user with restricted access can’t:
- Delete cases or linked items.
- Share the case with other users. Sharing and changing share permissions require the
case_management:editpermission through a workspace role, which gives access to all cases. A custom role withcase_management:editis no longer restricted: it sees every case in the workspace. - Create records that aren’t linked to a case. Records such as tasks and alerts must be linked to a case shared with them as
Editoror higher. - Create investigations or conclusions.
- Use case details, context, and historical cases, which require broader view access.
- Bulk update records other than cases.
Closing a case requires
Editor + Close. A user with only Editor can edit the case but can’t close it.Workflows, Agent Blink, and the API
Case-level permissions apply to users working in the Blink UI and through the API. Workflows work differently, and Agent Blink is partly covered:Other Behaviors to Know
- Group shares: a user gets the access granted to any group they belong to.
- Auto-provisioning: sharing with someone who isn’t in the workspace adds them with the Case Management Guest role. This doesn’t reduce a role they already have.
- Closed cases: closed cases block new comments and questions unless comments on closed cases are enabled in the Cases table settings.
- Notifications: a user is emailed when a case is shared with them, unless sharing notifications are turned off in the Cases table settings.
- History: sharing and unsharing are recorded in the case timeline and the audit log.
- Removing access: unsharing a case takes effect immediately.
Case Management Permission Hierarchy
When assigning case management permissions, it is important to understand how each permission relates to the others in terms of hierarchy:-
Having the
case_management:editpermission allows a user to create and modify cases. However, does not grant the ability to close (case_management:close_case) or delete (case_management:delete) cases. -
The
case_management:close_caseandcase_management:deletepermissions are considered higher in the permissions hierarchy.- Assigning a user the
case_management:close_casepermission automatically grants them the ability to close a case and edit cases (case_management:edit), even if that permission has not been explicitly assigned. However, it does not grant them the ability to delete cases (case_management:delete). - Similarly, assigning a user the
case_management:deletepermission automatically grants them the ability to delete cases and edit cases (case_management:edit), even without explicitly assigning that permission. However, it does not allow them to close cases (case_management:close_case).
- Assigning a user the
-
The
case_management:adminpermission sits at the top of the hierarchy. It grants full control over case management, including editing, closing, and deleting cases, as well as managing related settings.
Workspace Role Scope (Built in)
Owner
Users assigned the Owner workspace role have full administrative access to all cases and settings within the workspace. This role is intended for users who need complete control over case operations and configurations.The Owner user role is a built-in role available within the workspace role scope.
Owner Role Permissions
Owner Role Permissions
Contributor
Users assigned the Contributor user role can fully build and maintain workflows and case-related entities like tables, runners, and global variables. They have full edit access across case and workflow objects, including the ability to edit Case Management permissions, but cannot configure workspace settings.Contributor Role Permissions
Contributor Role Permissions
Viewer
Users assigned the Viewer user role only have permissions to observe existing cases, including any linked entities, without the ability to edit or create them.The Viewer user role is a built-in role available within the workspace role scope.
Viewer Role Permission
Viewer Role Permission
Case Management Guest
Users assigned the Case Management Guest role are granted view or edit permissions only for cases shared with the user and their groups, including any linked entities.The Case Management Guest user role is a built-in role available within the workspace role scope.
Case Management Guest
Case Management Guest
How to Create Custom Roles
The custom roles shown in this section are purely based on our recommendations for optimal visibility and usability. However, there is absolutely no obligation to follow these recommendations.
Clients have full control and discretion over how they choose to configure their custom roles. These recommendations are intended only as helpful guidance, your team is encouraged to customize the roles based on your specific needs, preferences, and workflows.
1
Navigate to Roles Settings
Navigate to the ‘Roles’ Tab, in settings and in the top-right corner, click on ‘New Role’ button in the top right-corner.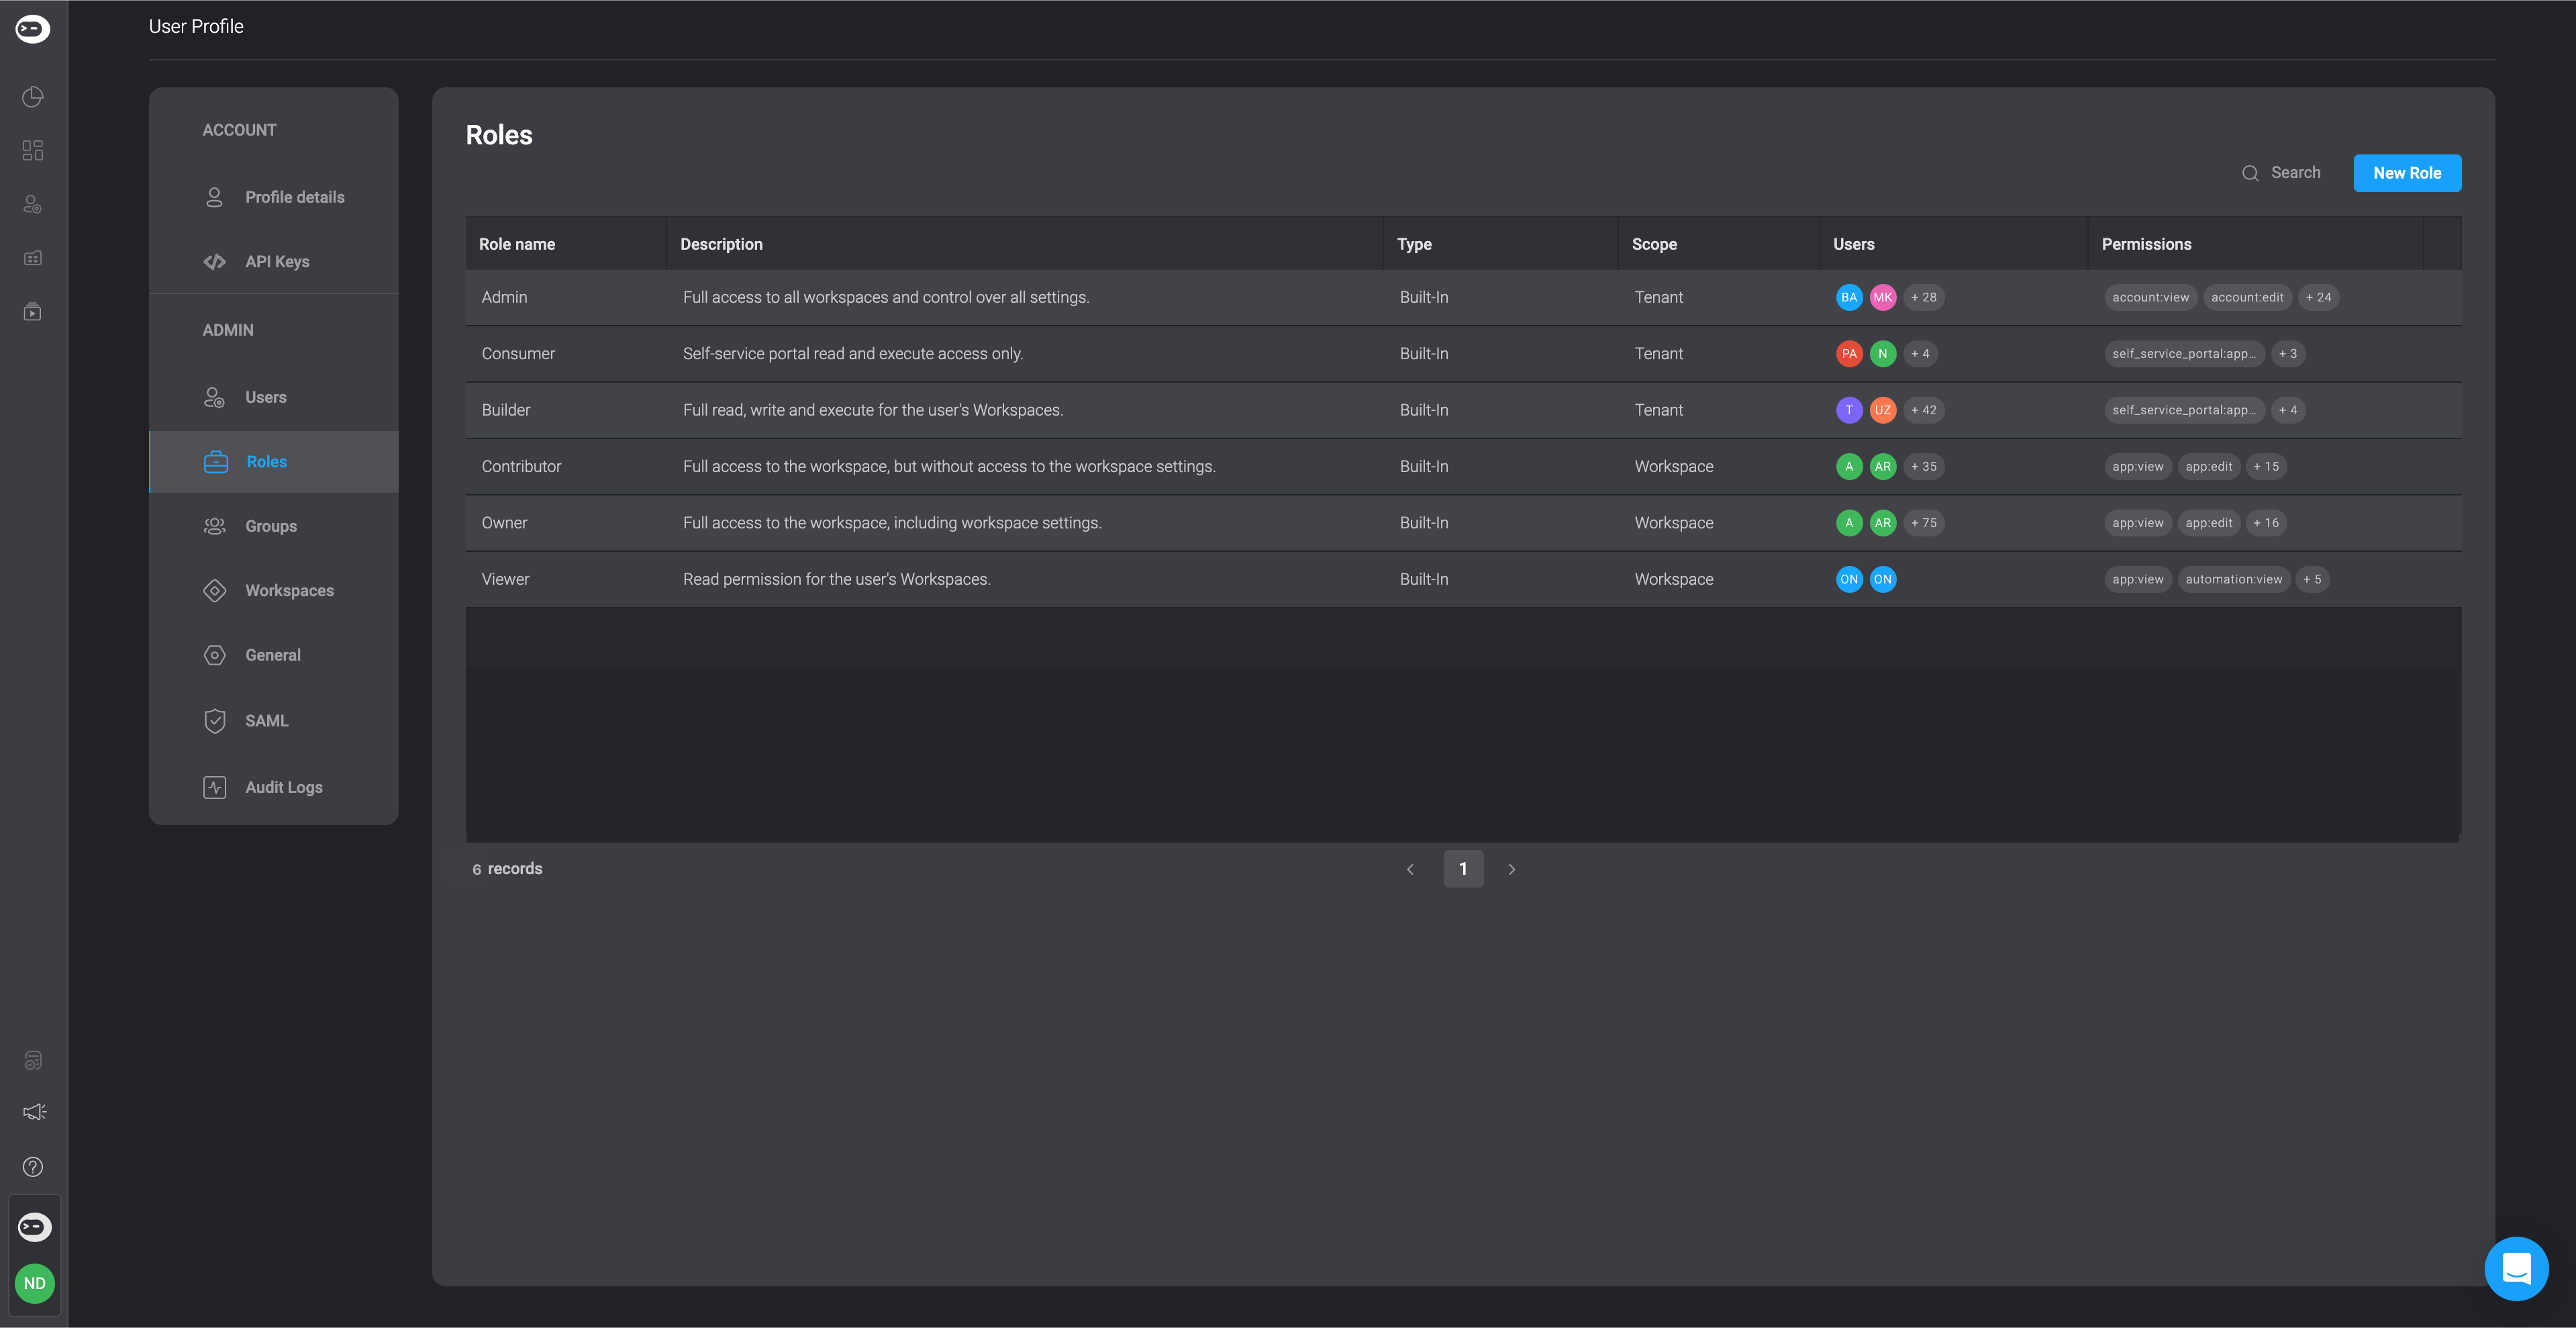
2
A dialogue box will open, displaying all user roles and their permissions.
3
Fill in the Necessary Details
Add a Role Name and a Role Description.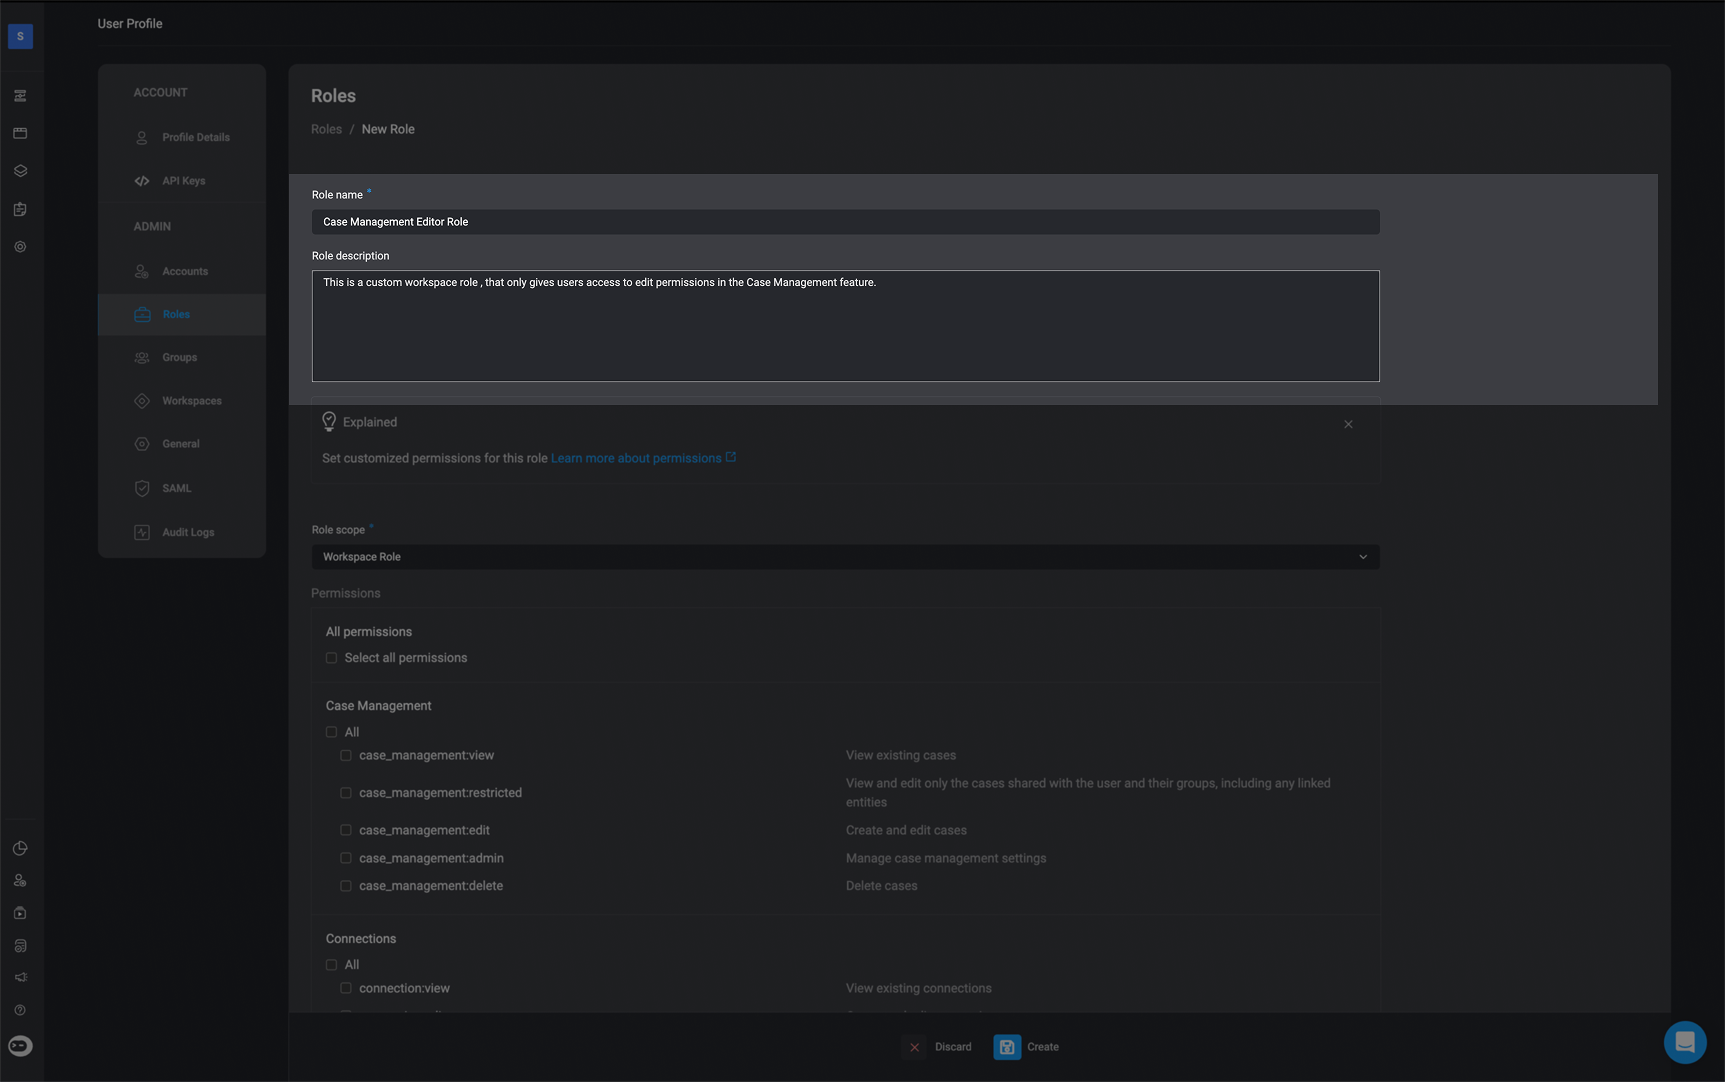
4
Choose the Workspace Role
Select the ‘Workspace Role’ option under the Role Scope section.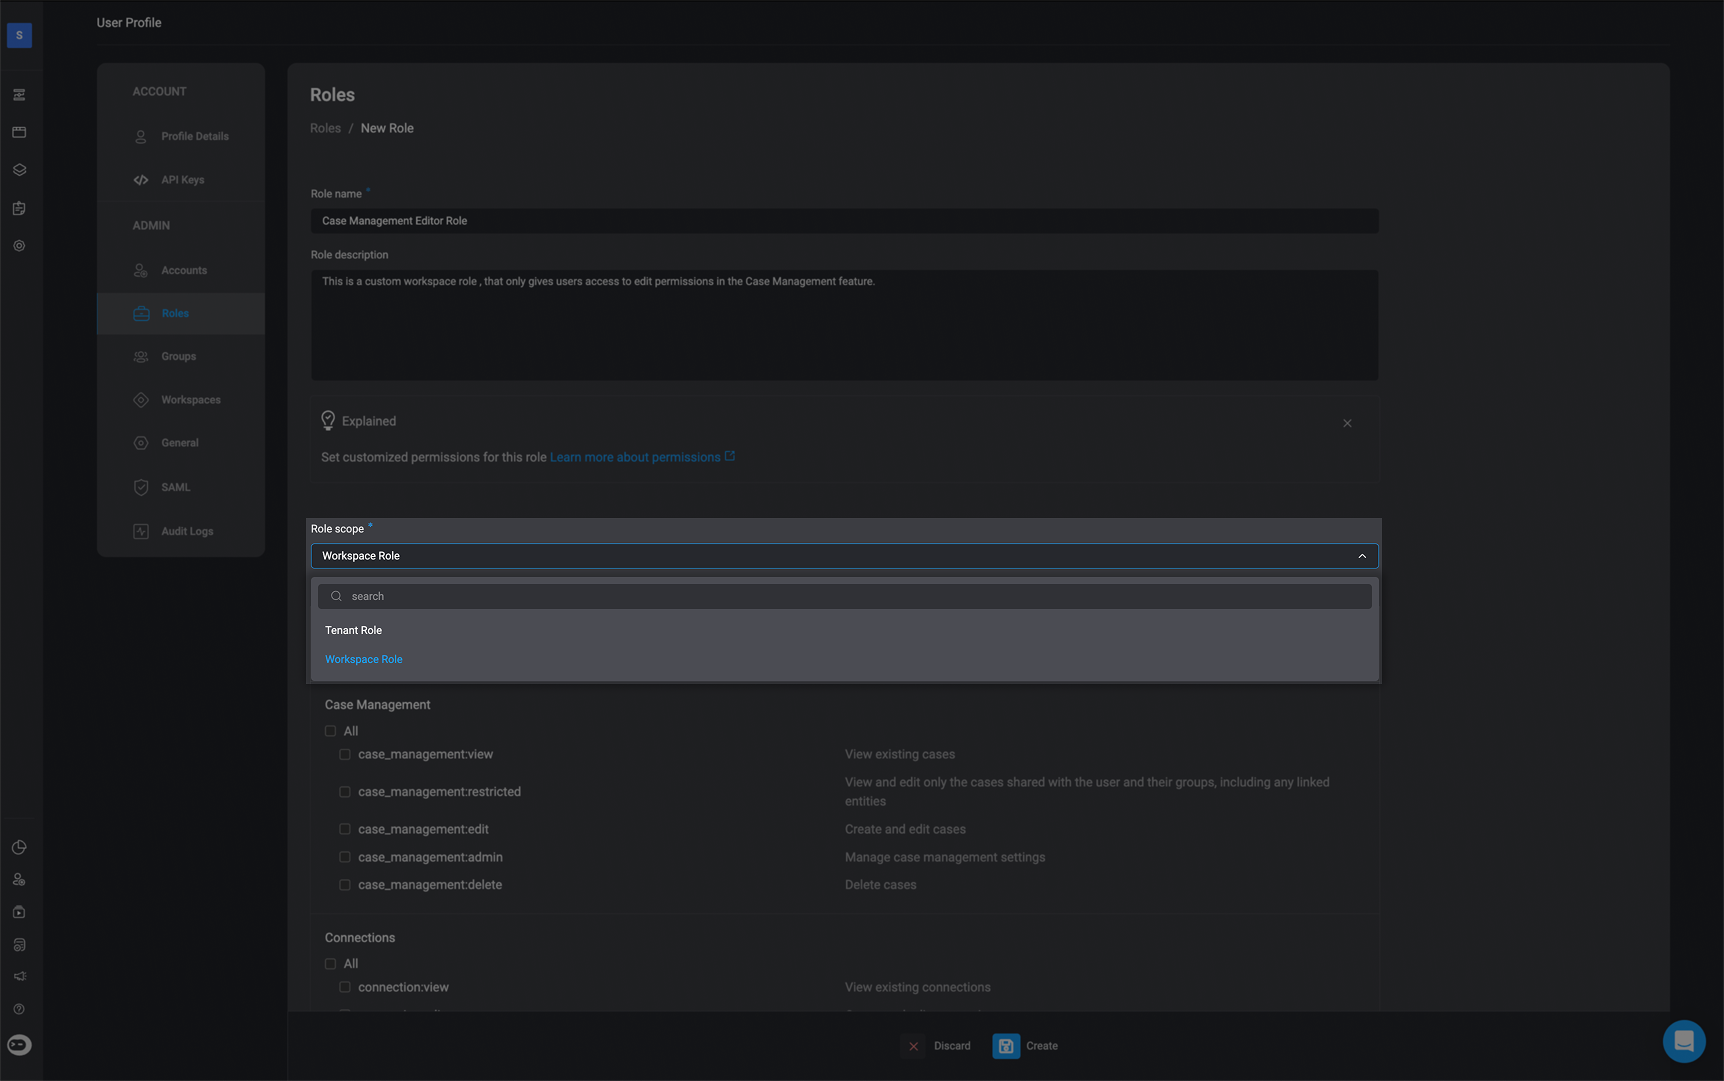
5
Choose Permissions
Choose permissions based on the custom role you wish to create
Workspace Role Scope (Custom)
The roles outlined below are custom role configurations designed to help you get started with managing permissions in your workspace. These are recommended templates based on common user needs and responsibilities, particularly within the Case Management feature. Use these custom roles as a baseline to guide your setup:SOC Analyst Role
Users assigned to the custom Case Management SOC Analyst user role can run workflows and manage cases but cannot edit workflows or system settings. They have full access to case creation and deletion, and read-only access to workflows, connections, and environment data. The custom SOC Analyst role will use the built-in Tenant Guest role on the Tenant Scope.Workspace Scope Permissions
Workspace Scope Permissions
Builder Role
Users assigned to the custom Case Management Builder user role can fully create and modify workflows and cases. They have broad access to build workflows, edit workflows, approve workflows and manage case data but limited access to workspace configuration. The custom Case Management Builder role will use the built-in Builder role on the Tenant Scope.Workspace Scope Permissions
Workspace Scope Permissions
Admin Role
Users assigned the custom Case Management Admin user role can fully build and maintain workflows and case-related features like tables, runners, and global variables. They have full edit access across case and workflow objects but cannot configure workspace settings. The custom Case Management Admin role will use the built-in Admin role on the Tenant Scope.Workspace Scope Permissions
Workspace Scope Permissions